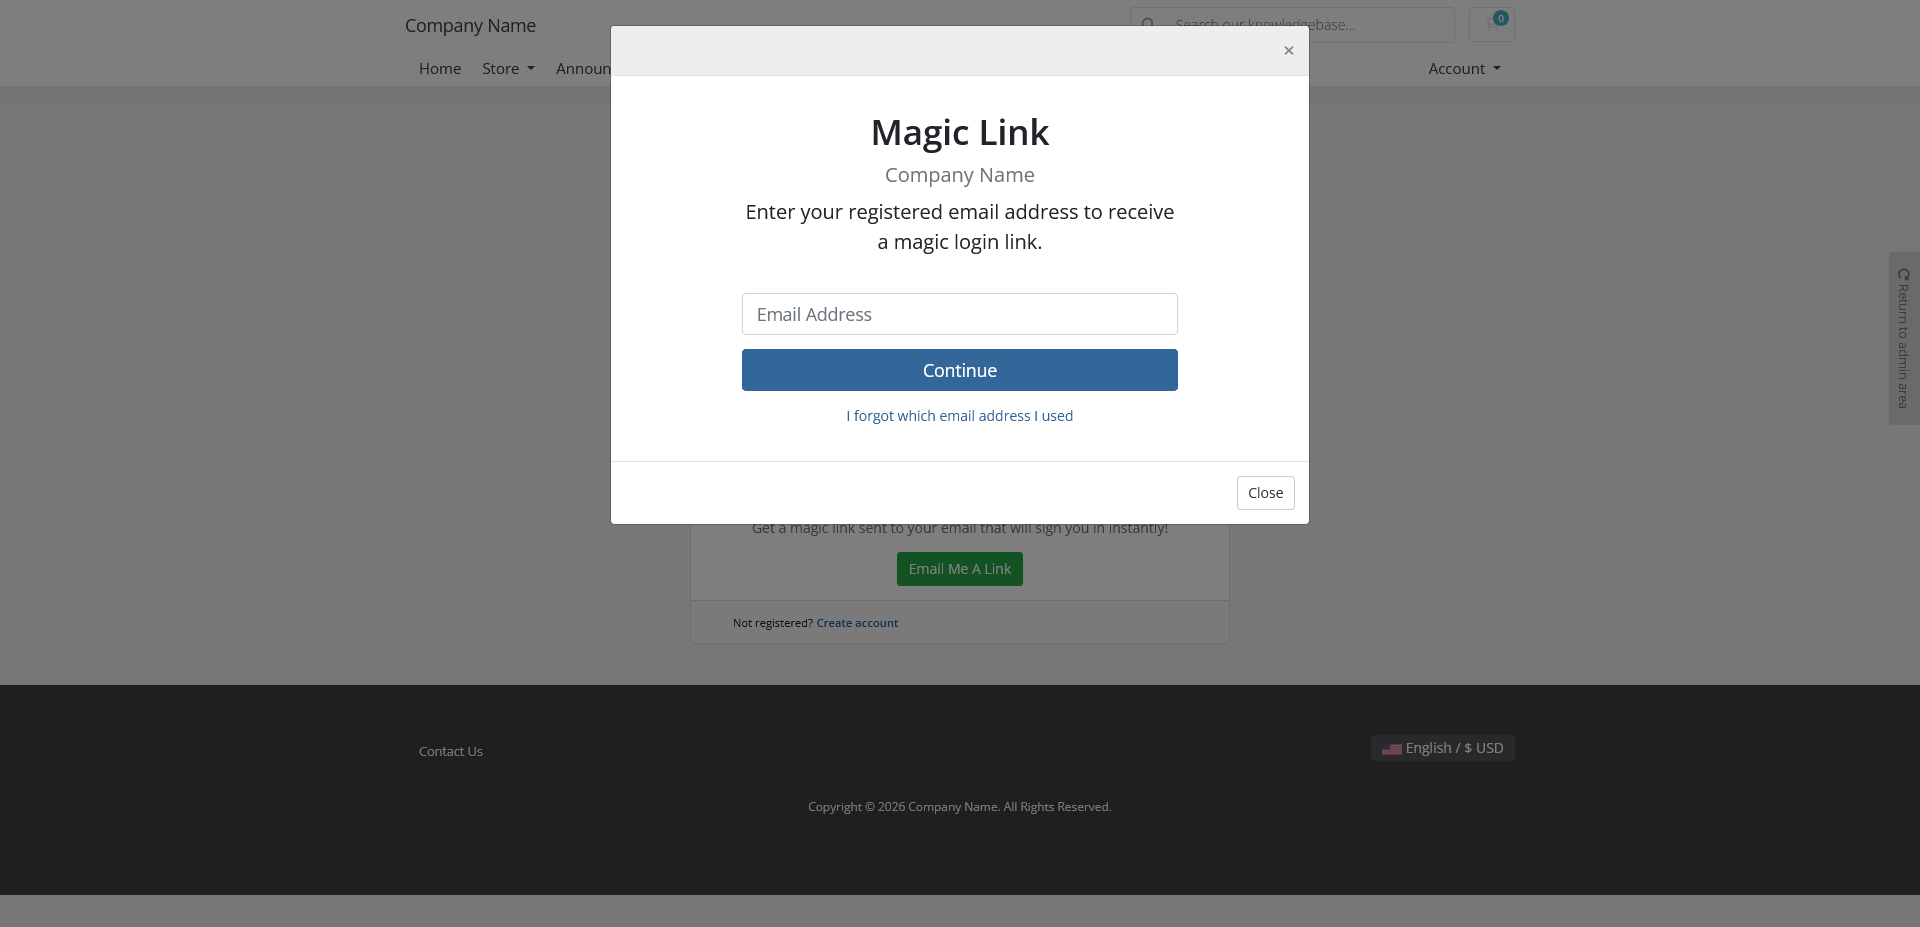
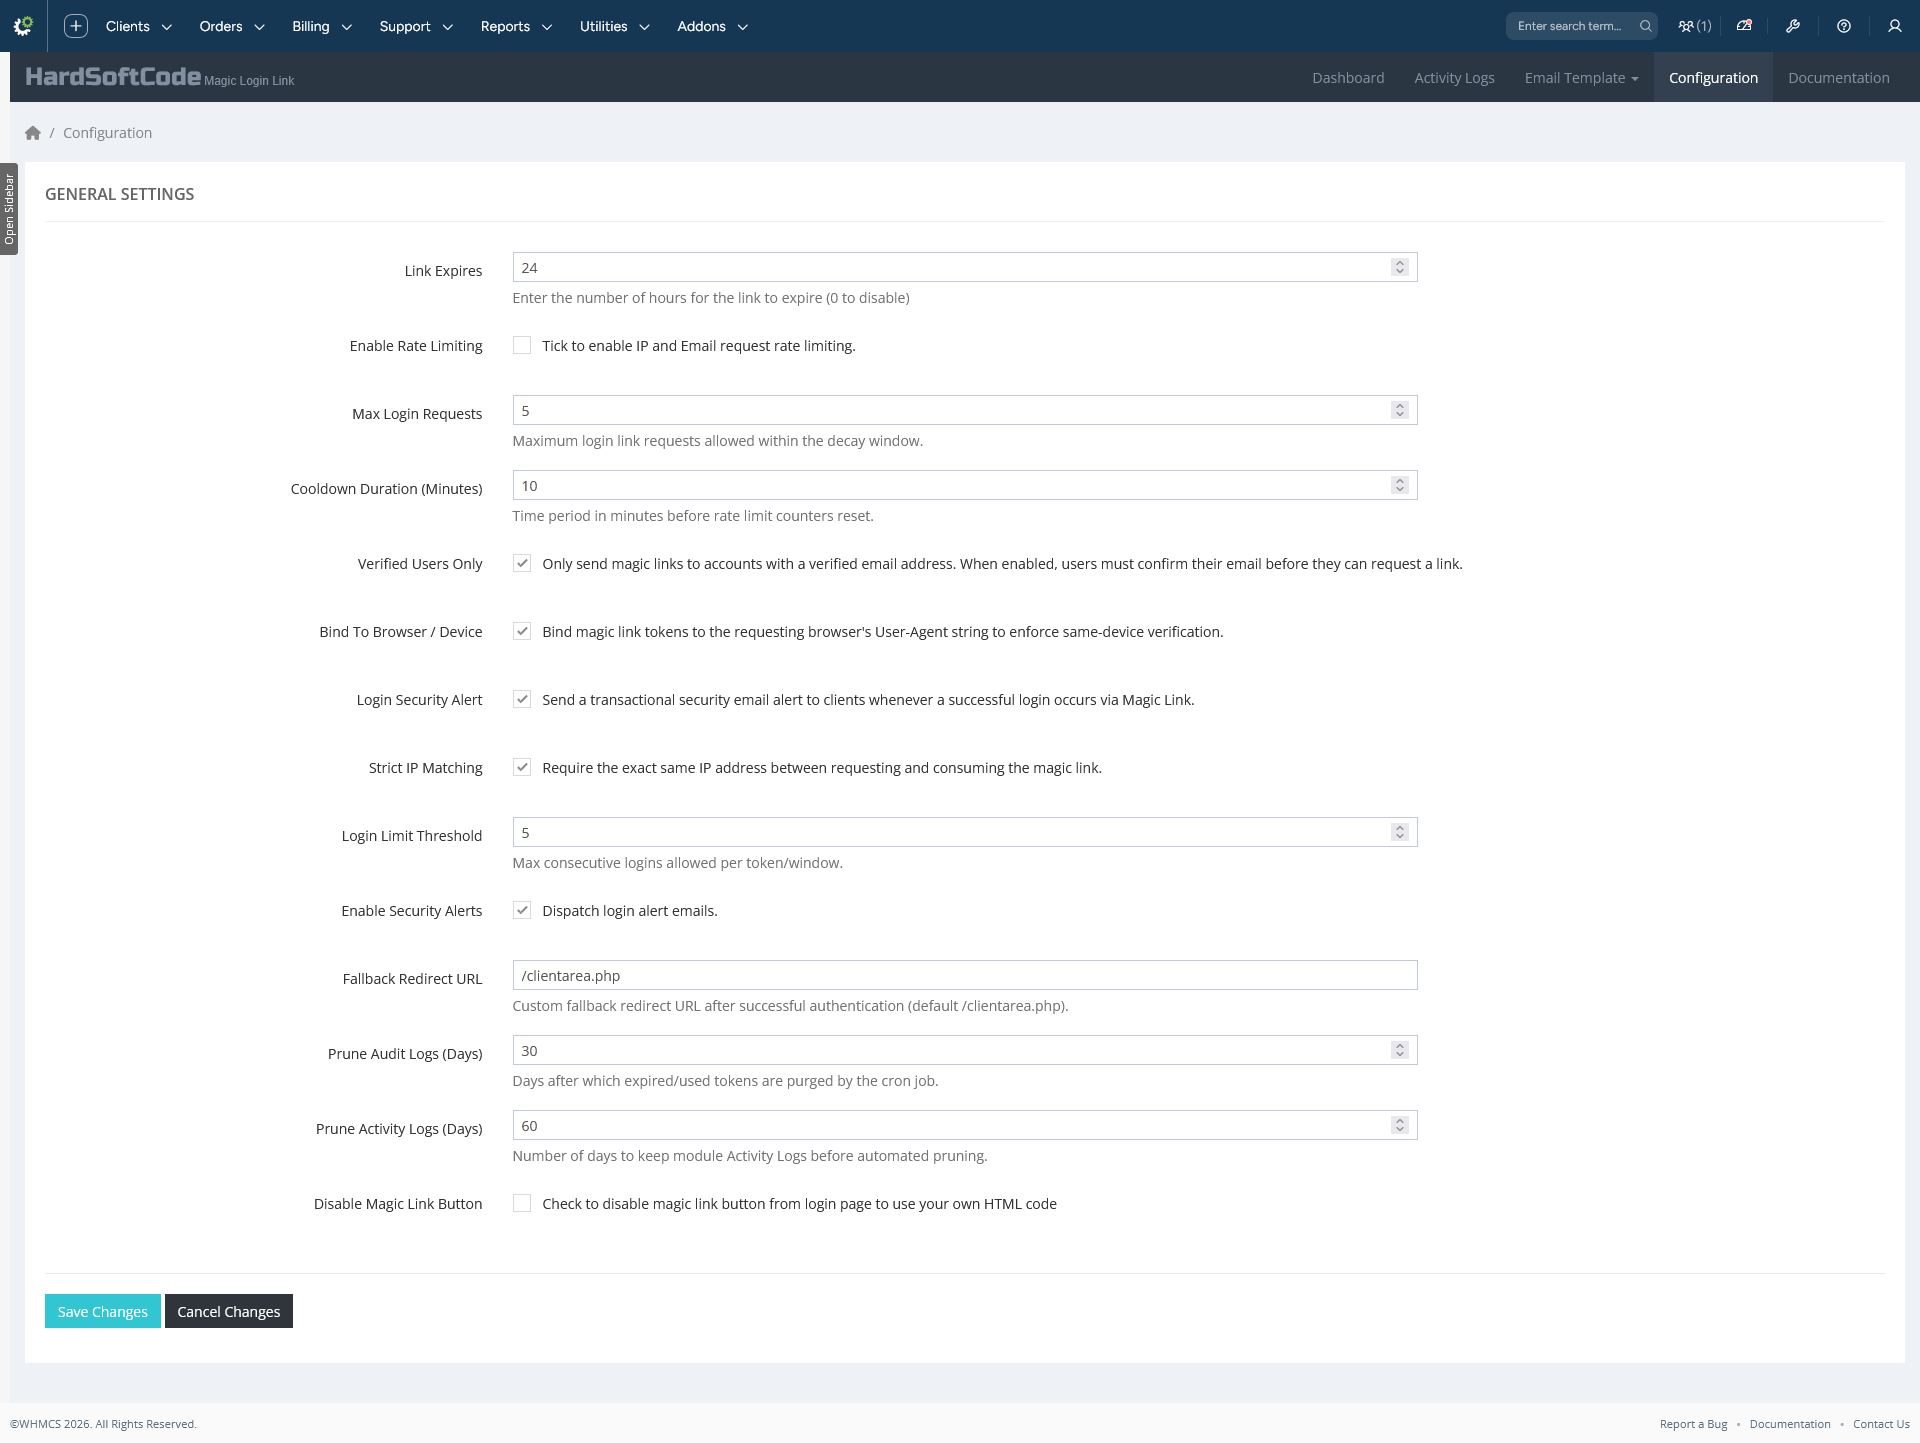
Magic Login Link

Magic Login Link

Developed By HardSoftCode

Compatible with WHMCS v9.0

A complete passwordless authentication addon for WHMCS that lets your clients log in to the client area with a single click — no password required. Magic Login Link sends a secure, time-sensitive login link straight to the client's email address; opening it signs the user in through WHMCS' native Single Sign-On engine.

The module eliminates login friction while keeping accounts thoroughly protected. Every token is single-use, expires automatically, is bound to the requester's IP address and browser fingerprint, and is protected by a built-in rate limiting engine (per-IP and per-email throttling with a configurable decay window). Clients can request a magic link themselves from the login page, and administrators can generate or send one directly from the Client Summary page or the Client Users table.

The addon ships with a full analytics Dashboard (token metrics, login trends, security events and system health), a dedicated Activity Logs screen with a filterable, server-side audit trail of every event, two ready-made email templates (Magic Link Request and Magic Link Security Alert) that install into WHMCS' email template editor with registered merge fields, and a single Configuration page for expiry, throttling, fingerprint binding, security alerts and automatic log pruning — everything governed by modern, secure, CSRF-protected admin screens.

What's new in v2.5

v2.5 adds full observability and tighter admin control on top of the existing passwordless login engine:

  • Module Activity Logs — a new dedicated audit screen (hsc_magiclink_activity_logs) recording every event with a severity level (success / info / warning / danger), the acting user or admin, IP address and browser/device. Events include token requests, admin sends, every email send (and failure), login successes and failures, IP / browser mismatches, rate-limit hits, manual invalidations and record deletions.
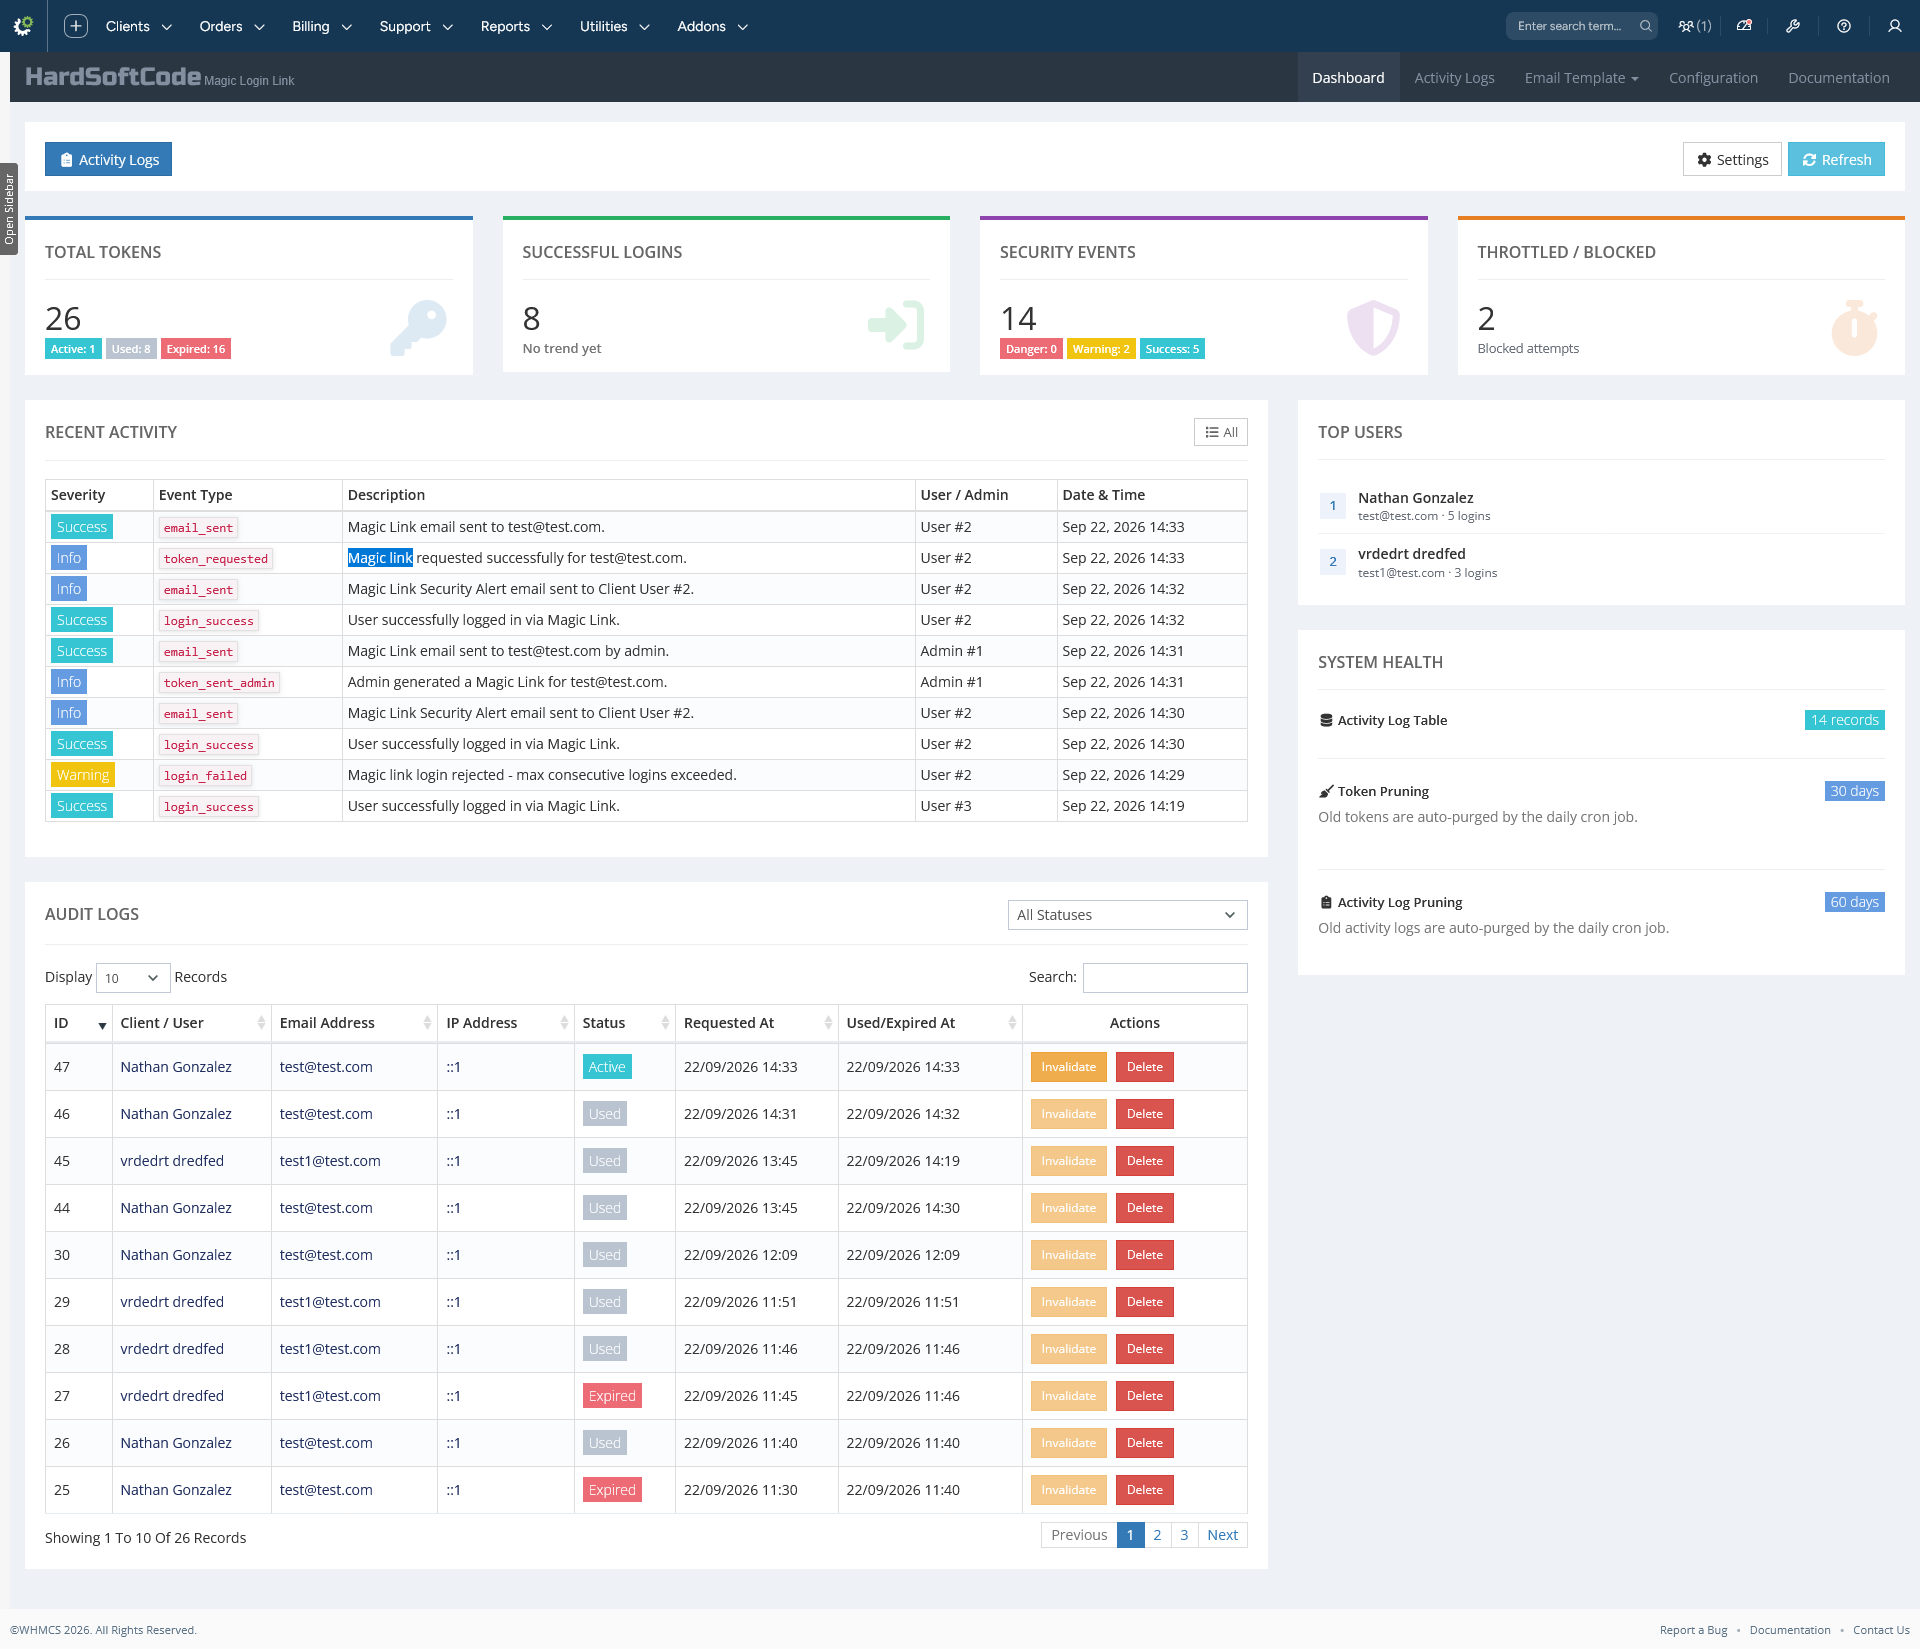
  • Analytics Dashboard — metric cards for token counts by status, successful logins with a month-over-month trend, security events, throttled/blocked attempts, top users by logins, recent activity, and a system health panel.
  • Audit table management — the Dashboard audit table now supports per-row Invalidate and Delete actions (AJAX, no page reload), and the Browser & Device column was removed for a cleaner layout.
  • Email send logging — every dispatched email (client request, admin send and security alerts) is recorded in the Activity Logs as email_sent / email_failed.
  • Automatic pruning — the daily cron job now also prunes old activity log rows (PruneActivityLogsDays), in addition to old tokens (PruneLogsDays).
  • Granular admin configuration — strict IP matching, login limit threshold, security alerts, fallback redirect URL and pruning retention are all configurable from the module's own Configuration page.

Features

Passwordless login

  • Login page button — a "Magic Login Link" button is injected automatically into the client-area login page (or provide your own custom button HTML). Clicking it opens a modal where the visitor enters their email address.
  • Single-use, expiring tokens — every magic link works exactly once and expires after the configured number of hours (default 24; 0 = never expires).
  • Native SSO sign-in — clicking the link logs the user in through WHMCS' CreateSsoToken API and redirects to a configurable destination (default /clientarea.php).
  • Account-enumeration safe — the request form always shows the same generic success response whether or not the email exists.

Security engine

  • Strict IP matching — require the login to come from the same IP address that requested the link.
  • Browser/device fingerprint binding — the requester's User-Agent is stored as a SHA-256 hash and must match at login.
  • Consecutive login limit — cap how many times a single token can be used in sequence; the counter resets when the user logs in with their normal password.
  • Rate limiting & cooldown — per-IP and per-email request throttling with a configurable decay window (enabled/disabled, max requests, decay minutes).
  • Automatic token invalidation — all active tokens are expired when the client or user changes their password.
  • Login security alert email — after every magic-link login the user receives a notification with the account, date & time, IP address and browser/device used (toggleable).
  • Sensitive email suppression — the EmailPreLog hook stops the magic-link email (which contains the login URL) from being stored in WHMCS' email logs.

Admin tools

  • Send / generate from the admin area — a "Send Magic Link" action link on the Client Summary page and in the Users & Permissions dropdown of the client users table: send the email instantly.
  • Dashboard analytics — token counts by status, lifetime logins with month-over-month trend, security event counts, throttled attempts, top users, recent activity feed and a system health panel (table presence + pruning retention).
  • Audit table actions — invalidate an active token or permanently delete an audit record straight from the Dashboard, with SweetAlert confirmation and AJAX table reload.
  • Activity Logs screen — server-side DataTable with global search, severity and event-type filters, severity badges, actor labels (User / Admin / System) and a per-row AJAX delete.

Email integration

  • Two ready-made email templates created on activation: Magic Link Request and Magic Link Security Alert.
  • Custom merge fields registered in WHMCS' email template editor: {$login_link}, {$login_url}, {$expire_time} (request) and {$login_ip}, {$login_time}, {$user_agent} (security alert).

Housekeeping

  • Daily cron pruning — old used/expired/invalidated/failed tokens and old activity log rows are removed automatically after the configured retention days.

We also offer full source code licenses for all of our products. Source code access for Magic Login Link is available for $280 USD. Please contact our support team for further details or to request a purchase.


Reviews

5 stars
0
0
4 stars
1
1
3 stars
0
0
2 stars
0
0
1 star
1
1
Arjen Kocken avatar

Arjen Kocken @arjen4010

February 16, 2021 at 12:00:27 AM

I did not try this module at the moment, I'm thinking about it. But first I want to say something about this conversation, we use some modules from Hard Soft Code, and they are all working as expected and are available in the client area. So I can't find me in his reaction.

A question about the product, it's looking like a solution for people that can't remember password or still writing it on paper, they also write it down when you told them 1000x to don't do that. But ok, I think more people can agree this problem.

About the security of this, is it possible to disable this option by default and give the client the possibility to turn it on from the client area? I can think that some clients will be happy with this solution, but I think some other customers see it as a security issue. The best will be if they can set a permission per contact, let's say the one that pays invoices "yes", the developer "no".

Another idea will be if it's working in combination with the Authy module: https://marketplace.whmcs.com/product/846-authy-security-module

And for me the idea of 24 hours is way to long, also 1 hour feels for me like a issue. Any idea to also add options like 5, 15, 30 min? If there is a solution for both, I will really think about using it.

  • 5 years ago
  • Version Number 1.1.0
  • Edited
Chris . avatar

Chris . @chris8303

November 17, 2020 at 11:44:15 PM

Total con stay away from these guys. Purchased and didn't work, also invalidated the licence a day later and deleted my account. Stay well away!

HardSoftCode Teams avatar

HardSoftCode Teams @HardSoftCode

November 18, 2020 at 12:38:01 AM

Be aware of this buyer. After buying from us and download the module he go and open a paypal claim and says that he did not received the module and we have close his account

Owner@HardSoftCode  
  • 5 years ago
  • Version Number 1.1.0

Version Compatibility


Compatible with WHMCS v9.0

Full Version Compatibility


  • All versions of WHMCS v9.0
  • All versions of WHMCS v8.13

System Requirements


  • PHP 8.1+
  • IonCube Loader v14.0+
  • WHMCS native Single Sign-On feature available
  • The daily cron job must be configured (standard WHMCS cron)

* Requirements listed are in addition to the WHMCS default system requirements.

Support for this product

The best place to start if you need help with a specific product is to contact the developer. All WHMCS Marketplace developers have both a website and support URL listed.

Developed By HardSoftCode

Changelog

v2.5.0 Released September 22nd, 2026

Latest Version


Module Activity Logs & observability

  • New Activity Logs screen: server-side DataTable with global search, severity and event-type filters, severity badges, actor labels and metric cards (total events, failures, admin/user actions).
  • New hsc_magiclink_activity_logs table recording every event: token_requested, token_sent_admin, email_sent, email_failed, login_success, login_failed, token_invalidated, tokens_invalidated, token_deleted, rate_limit_exceeded, user_agent_mismatch, ip_mismatch.
  • Every email send is logged — client requests, admin sends and security alerts record email_sent / email_failed in the Activity Logs.
  • Analytics Dashboard — token counts by status, successful logins with month-over-month trend, security events, throttled attempts, top users, recent activity and a system health panel.
  • Audit table actions — per-row Invalidate (AJAX) and Delete (AJAX with SweetAlert confirmation, no page reload); deleting a record writes a token_deleted entry to the Activity Logs. The Browser & Device column was removed from the audit table.
  • Automatic activity-log pruning via the daily cron (PruneActivityLogsDays, default 60 days).
  • Active menu highlighting on all module admin pages.
  • Admin configuration page with granular settings: Strict IP Matching, Login Limit Threshold, Security Alerts toggle, Fallback Redirect URL and token pruning retention (PruneLogsDays, default 30 days).
  • Daily cron job now auto-prunes old used/expired/invalidated/failed tokens.
  • Login Security Alert email — after every successful magic-link login the user receives a notification with account, date & time, IP address and browser/device (EnableLoginSecurityAlert).
  • New Magic Link Security Alert email template with {$user_email}, {$login_time}, {$login_ip}, {$user_agent} merge fields.
  • Browser & device fingerprint binding — the requester's User-Agent is stored as a SHA-256 hash (user_agent column) and validated at login (BindUserAgent).
  • Token status migrated from a legacy integer flag (0/1) to string states — active, used, expired — enabling proper single-use/expiry lifecycle management.
 

Previous Versions


v1.1.0 Released September 16th, 2020

View/hide detailed changelog

  • Added support to WHMCS v8.0 and PHP v7.4
  • Removed TPL overwrite function
  • Replace ClientLoginShare hook with Single Sign-on API
  • Improve by allowing users to login


v1.0.0 Released April 4th, 2020

View/hide detailed changelog

  • Initial release


See also

Terms of Service

This module allow you to add a page for your terms of use and you can add description and keyword
Free
Favicon Manager

Favicon manager module lets you add a favicon image to your WHMCS website.

Free
Social Login

Social Login is a free WHMCS plugin that allows your visitors to comment, login and register with 40+ social networks like for example Twitter, Facebook, LinkedIn, Instagram, Google and Yahoo.
Free
Privacy Policy

This module allow you to add a page for your privacy policy and you can add description and keywords
Free
Sitemap Generator

Generates dated XML sitemap including Products and Knowledgebase with cron and management options.
Free