Changelog
vv2.0.0
Released September 22nd, 2026
Latest Version
Changelog — Didit KYC Verification for WHMCS
v2.0.0 — September 2026
A complete rebuild on the new Tivro framework, with a new admin panel, stronger security, identity matching and full GDPR tools.
Highlights
- Redesigned admin panel: Overview, Verifications, Rules, Settings, Logs and License
- Identity Match: the name and date of birth on the ID must match the WHMCS profile
- Built-in date of birth field, editable by clients and admins
- Provisioning is held automatically until the client is verified, then released on approval
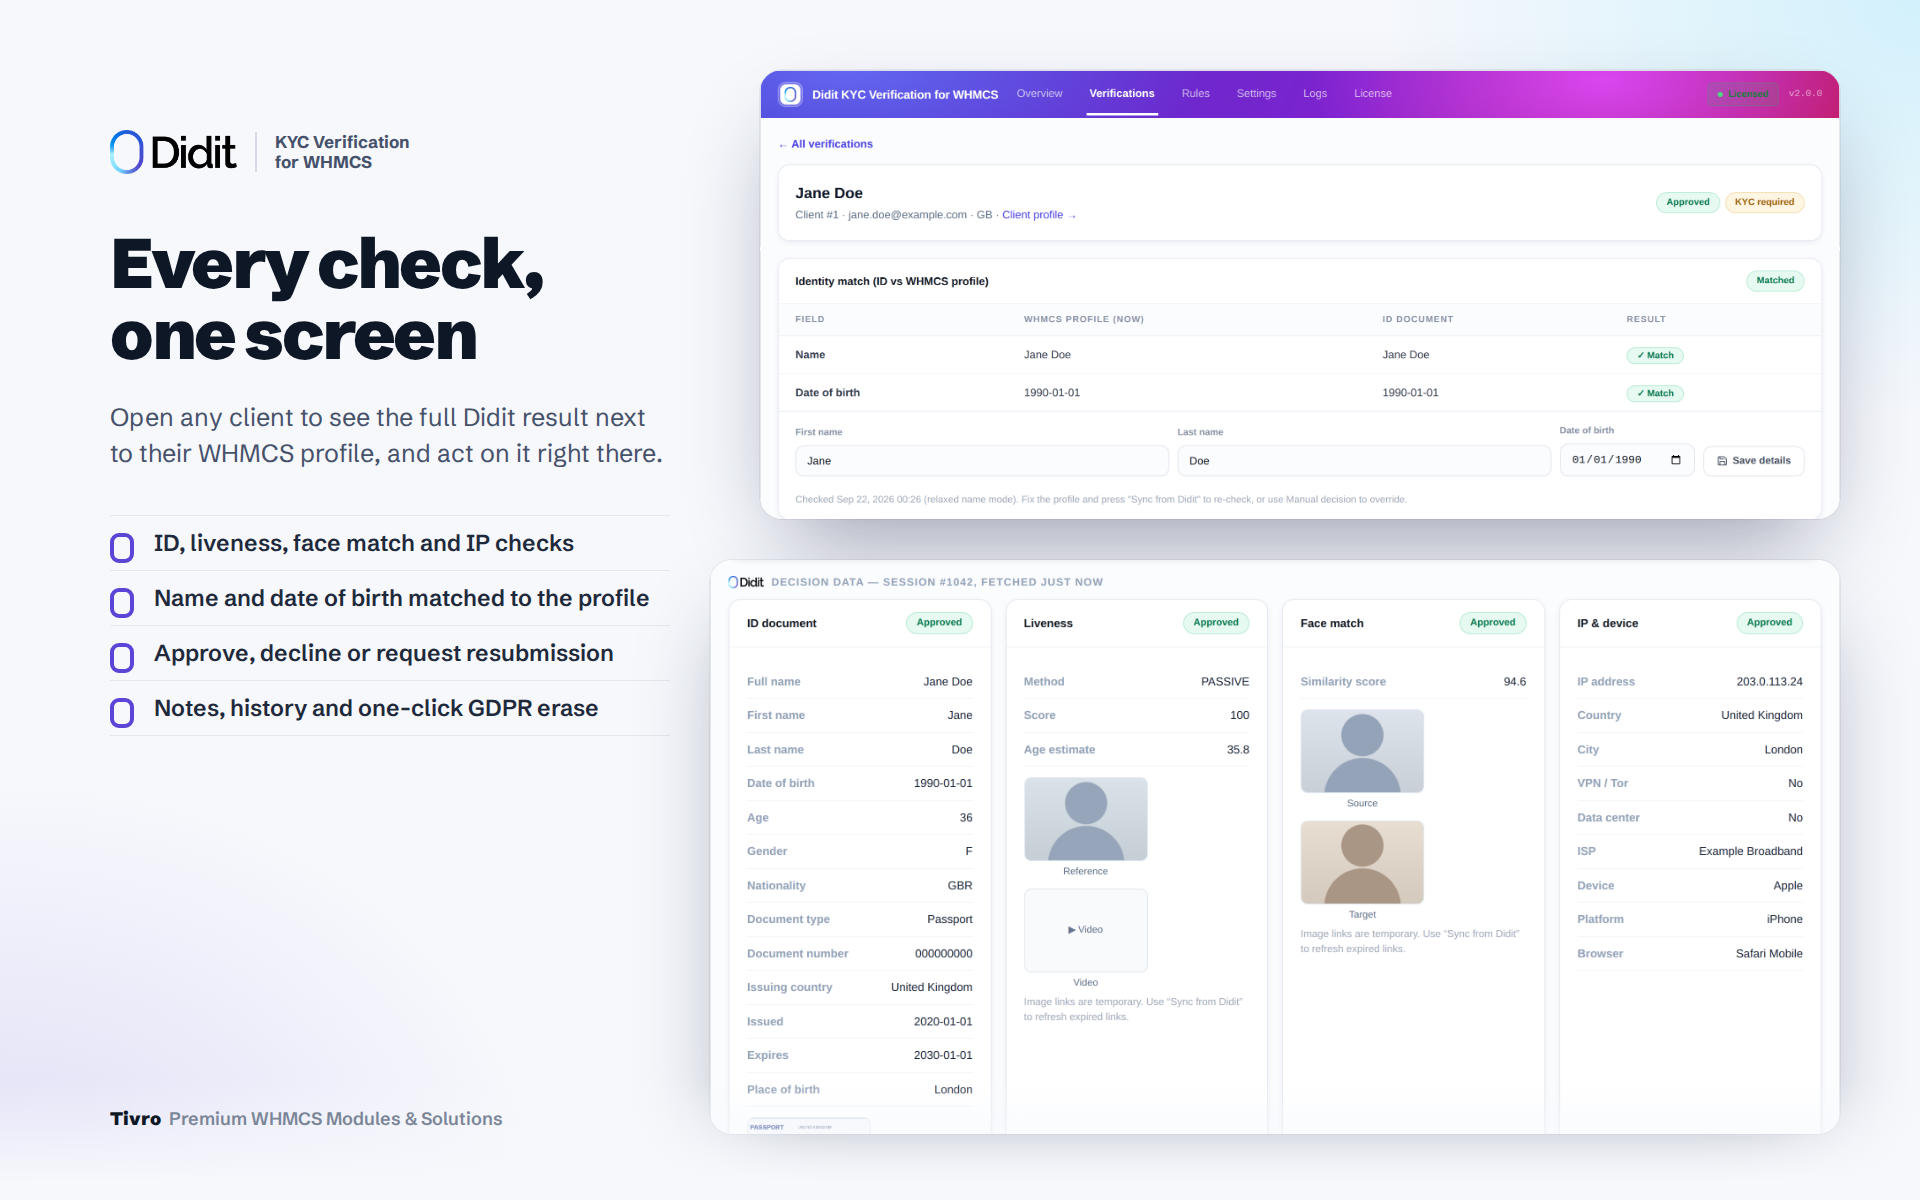
- Full decision viewer for ID data, images, liveness, face match, AML and IP/device checks
- One-click import from the old Didit KYC addon
Added
Identity Match
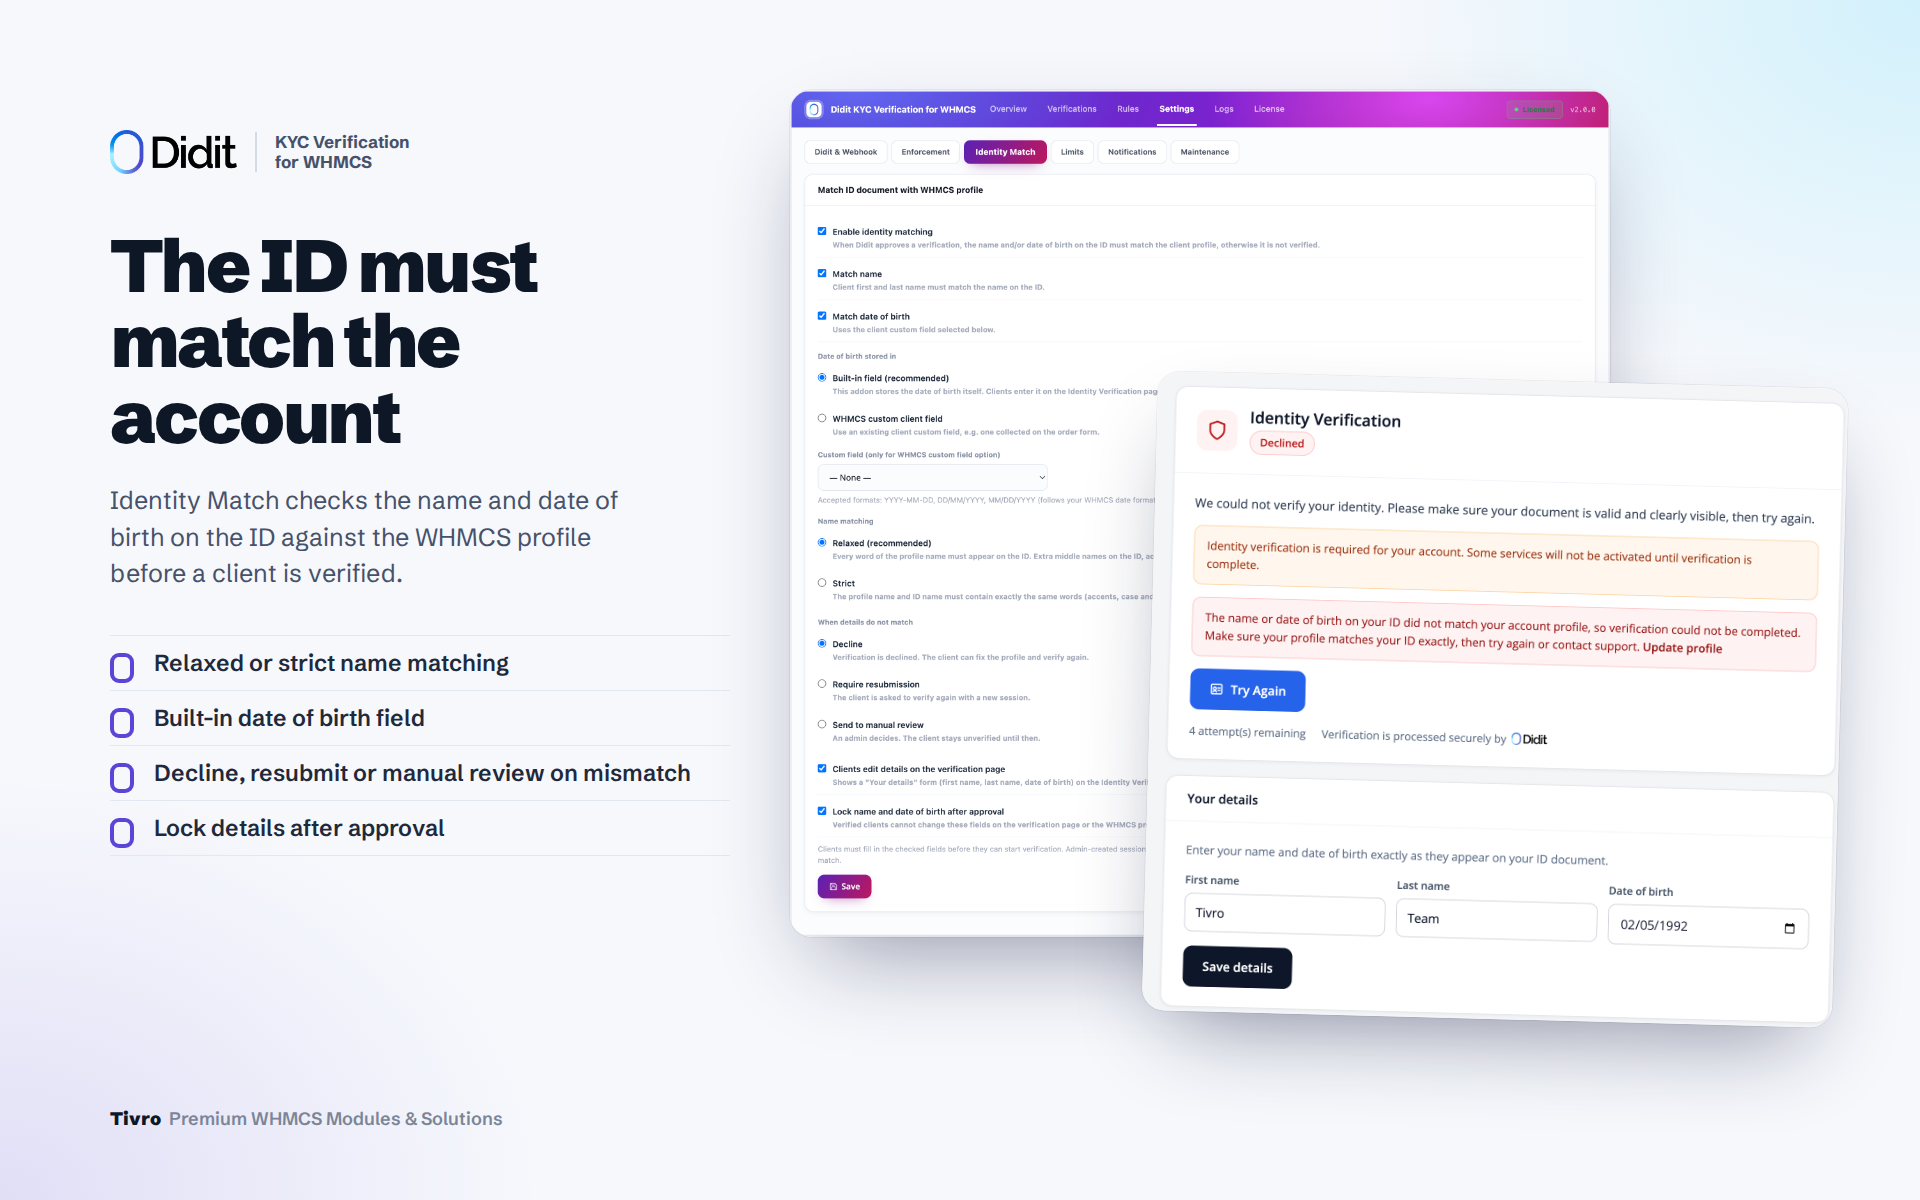
- Compares the name and/or date of birth on the ID with the client profile when Didit approves
- Relaxed or strict name matching; accents, case, hyphens and word order are ignored
- On mismatch, choose to decline, require resubmission or send to manual review
- Clients must complete their details before they can start verification
- Optional lock that stops name and date of birth changes after approval
- Admin comparison card shows profile vs ID with a ✓ or ✗ per field
Client details and date of birth
- "Your details" form on the verification page updates the WHMCS profile
- Built-in date of birth field, or use an existing WHMCS custom field
- Admins can edit a client's name and date of birth from the verification page
Enforcement
- Four modes: notify only, block checkout, hold provisioning, or both
- Held services are tracked individually and provisioned automatically on approval
- Admins can provision or discard held services manually, with optional admin bypass
- Rules by client group, product, product group, country or order total, each with its own Didit workflow
- Per-client exempt and lock flags
- KYC can expire after a set number of days, with an expiry email
Admin
- Dashboard with live metrics, review queue, system health, held services and recent activity
- Verification list with search, filters, date range and full CSV export
- Verification detail page:
- Manual approve, decline or resubmission request, with a reason
- Sync from Didit, and create a new session with a shareable link
- Internal notes, status history and activity timeline
- Complete Didit decision data with temporary document images and raw JSON
- KYC badge on the WHMCS client summary and order pages
- Webhook URL with a copy button and a signed self-test
- API connection test that reports real errors
- Logs for activity, webhooks, API calls and status changes
Client area
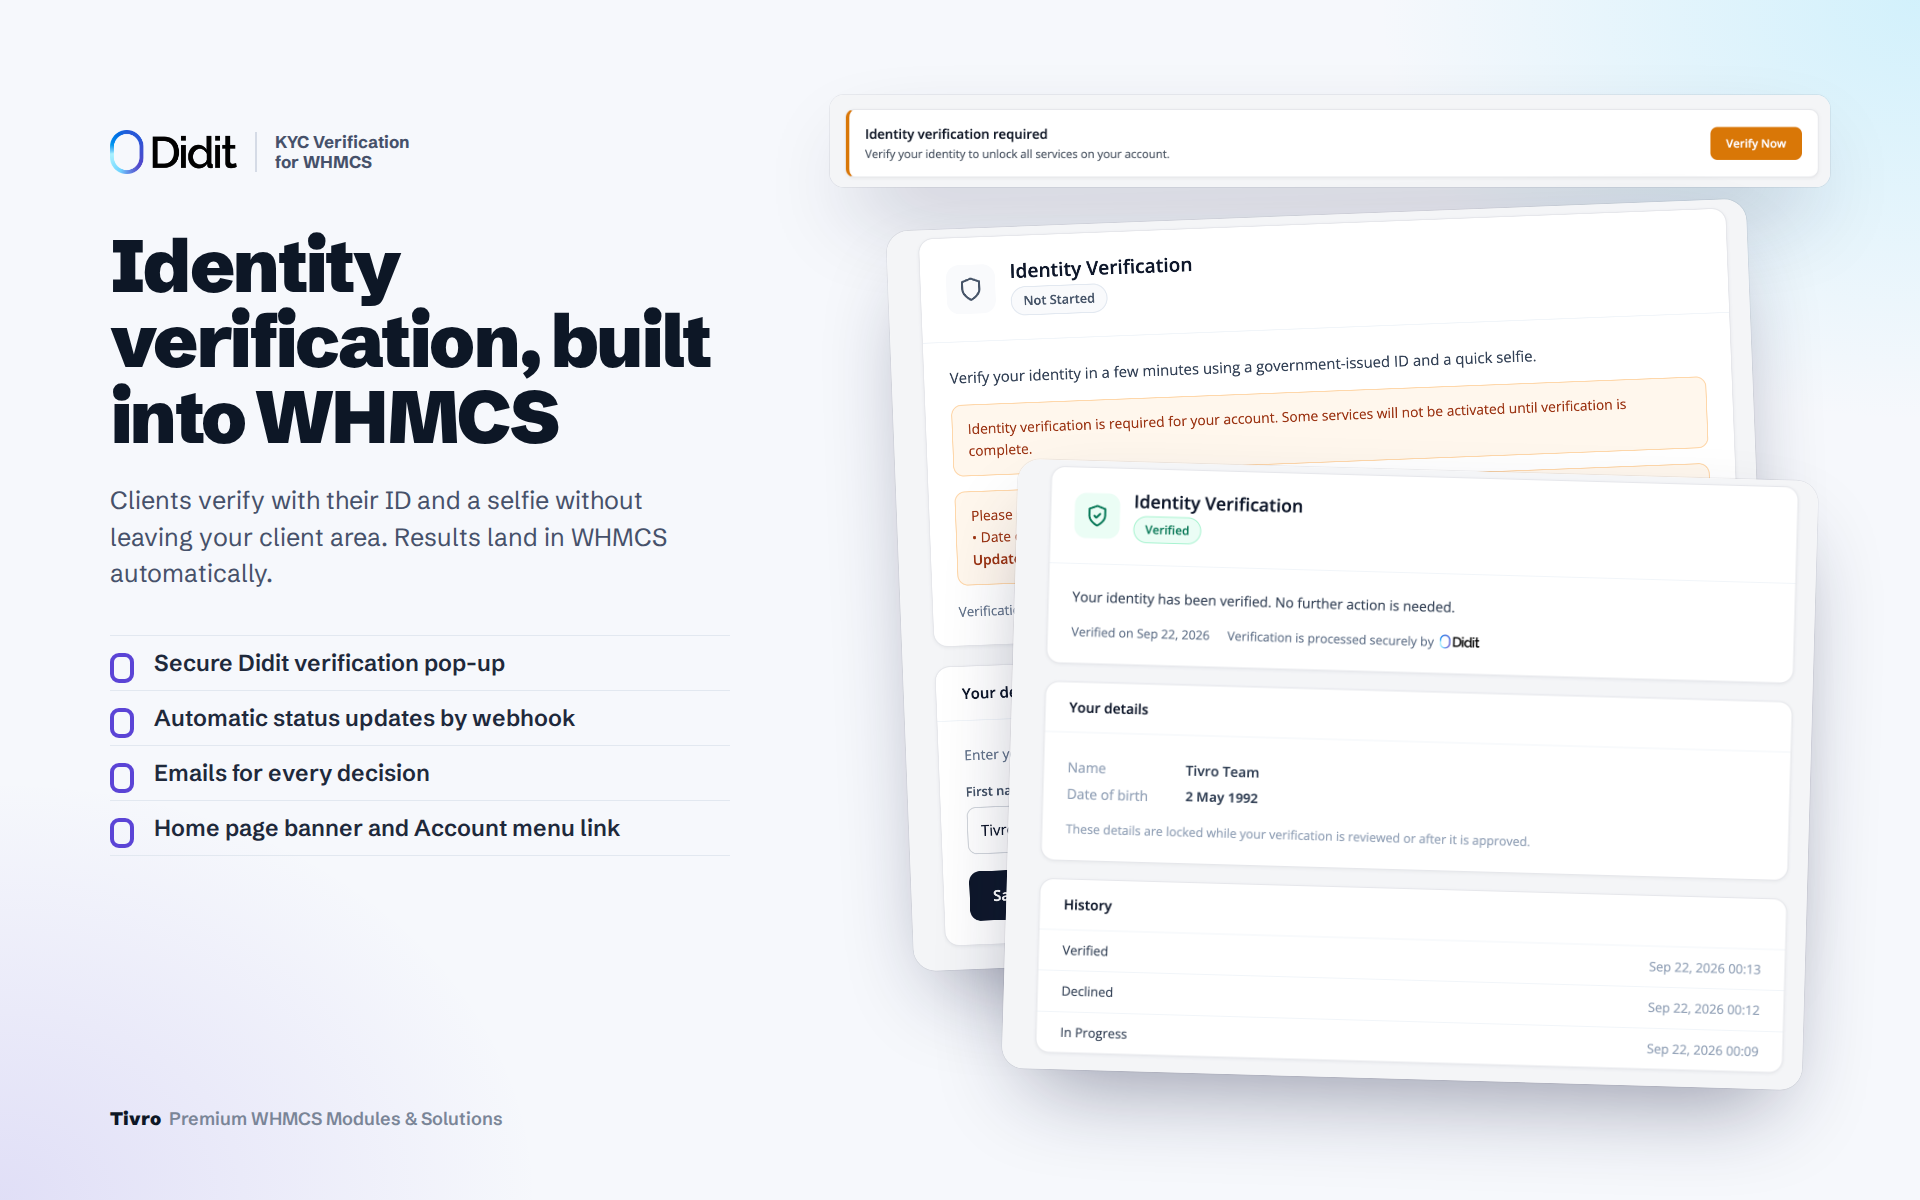
- Redesigned verification page with clear status, steps and history
- Secure verification pop-up, with an open-in-new-tab fallback for camera issues
- Home page banner (only for clients who must verify) and an Account menu link
- All text is translatable
Emails
- WHMCS email templates for Approved, Declined, Resubmission Required and Expired, each switchable on or off
- Admin alerts for declined, in review and resubmission cases
Privacy and GDPR
- One-click erase of all stored KYC data for a client, optionally deleting the sessions at Didit too
- Debug logging (full request and payload bodies) is off by default
- Configurable log retention with automatic daily cleanup
Cost control
- Unfinished sessions are reused instead of creating new paid ones
- Cooldown between sessions, a daily limit and a maximum number of attempts per client
- Duplicate clicks can't create duplicate paid sessions
Security
- Webhooks are rejected unless a secret is configured (previously anyone could approve a client)
- Verification status is always confirmed with Didit's API, never taken from the webhook message
- Webhooks for unknown sessions are ignored instead of creating verifications
- The client ID in each webhook must match the session owner
- Replayed and duplicate webhooks are blocked (timestamp check and duplicate detection)
- The API key and webhook secret are stored encrypted and never shown in the page source
- CSRF protection on every admin and client action
- Error messages no longer expose client IDs, file paths or line numbers
- The client verification script no longer injects raw HTML, closing an XSS risk
- CSV exports are protected against spreadsheet formula injection
Fixed
- The master "enabled" setting was never read correctly
- The daily cron crashed
- Approval force-activated all of a client's pending orders; now only held services are provisioned
- The order hold and service suspension didn't work
- The approval event hook never fired
- Product and order-total rules never matched
- Per-rule workflow selection was ignored
- Statuses could move backwards, and the approval date was overwritten on repeat webhooks
- Admin decisions were overwritten by later Didit webhooks
- The verification pop-up closed itself while the client was still verifying
- The banner showed to clients who didn't need verification
- The CSV export was missing emails and only exported one page
- The API connection test reported success on errors
- Settings were lost when the addon was deactivated
- The admin link from the order page was broken
Removed
- Non-working affiliate withdrawal hook
Under the hood
- Moved to the new Tivro framework with a single entry point for all requests
- The database schema updates itself automatically after file uploads
- License management fixes: the deactivate button works, and the License page is reachable when unlicensed
Upgrading from the old Didit KYC addon
- Upload and activate Didit KYC Verification for WHMCS.
- Enter your license key, then your Didit API key, webhook secret and workflow ID.
- Go to Settings → Maintenance → Import legacy data.
- Update the webhook URL in the Didit console and press Send signed test webhook.
- Deactivate the old addon.
Previous Versions