eKYC Guard — Identity Verification & Fraud Prevention for WHMCS

eKYC Guard — Identity Verification & Fraud Prevention for WHMCS

Developed By Arahoster

Compatible with WHMCS v9.1

Stop fraud before it provisions

eKYC Guard holds services and domains until the customer has verified their identity. Stolen cards, fake sign-ups, phishing sites and spam VPS orders stop at the gate, before they cost you a chargeback, an abuse report or a blacklisted IP range.

Genuine customers finish in a few minutes. You decide who has to verify, when, and what happens if they don't. The gate, every enforcement action and every new check ship switched off, so installing the module changes nothing until you turn it on.

Why hosting companies use it

  • Fewer chargebacks. People paying with a stolen card rarely finish a selfie and ID check, so the order never gets provisioned.
  • A clean network. No server is created for an unverified customer, so fewer abuse reports reach your data center.
  • No extra friction for good customers. Verify only first orders, large orders, high fraud scores, risky IPs or selected products. Everyone else checks out as usual.
  • Your staff can see who is verified. A banner in support tickets shows the client's status before anyone resets a password or hands out an EPP code.
  • It runs by itself. Invitations, reminders, grace periods and, if you want them, suspension. With auto-provisioning on, paid orders that were held are created the moment the customer passes.

New in 1.8.0

Fraud checks. Each check has its own switch and its own action: flag, send to review, or reject.

  • Same person, new account. Recognises someone you rejected or banned who comes back on a fresh account. It compares a keyed fingerprint of the document number, or the name and date of birth. The numbers themselves are never stored.
  • Name match. Compares the name on the ID with the client profile, contacts, the billing name on saved payment methods and PayPal/Stripe payer names.
  • Company check (KYB). Looks up business customers in Norway's Brønnøysund Register, EU VIES and UK Companies House, and flags companies that are missing, closed or registered under another name.

Smart triggers. Require KYC only when an order meets your conditions: the customer's first order, an order total above an amount, a WHMCS fraud score above a value, or a client who signed up recently.

Verification for sensitive actions. Require a verified identity before a customer gets an EPP transfer code, unlocks a domain, changes domain contacts or the account email, changes a service password, or runs service buttons such as rebuild or reinstall. Each action has its own switch.

Instant alerts. Get notified on Telegram, Slack, Discord or a signed webhook when a review is waiting, a check finds something, or an order is held. There's a test button, and customer names are included only if you allow it.

Continue on your phone. A QR code on the verification page lets the customer take the photos with their phone camera, without logging in there. The link works once and expires.

Statistics. See the acceptance rate, time to a decision, customers who stopped half-way, and what each provider costs you, for 7, 30, 90 or 365 days.

Everything in eKYC Guard

7 verification providers + manual review

  • Didit: ID document + liveness in 220+ countries, with an optional business (KYB) workflow for company accounts
  • DigiLocker (India): government-backed verification (OAuth2 + PKCE)
  • Stripe Identity, Sumsub, Onfido, Persona, Shufti Pro
  • Manual review: customers upload their documents (desktop or phone camera) and your team approves or rejects. Admins can also upload on a customer's behalf.

Turn on one provider or several, and customers choose. Decisions arrive by signed webhook. For Didit, Stripe Identity, Persona and Onfido, a daily check also picks up any webhook that was missed.

Provisioning gate

  • Holds service creation, domain registration and transfer, and orders at checkout until the customer is verified
  • Auto-provisions paid orders and services that were held the moment the customer passes, with the normal WHMCS welcome emails (optional)
  • Admins can override the gate when needed; every override is logged
  • Choose how the client area behaves: no gating, a banner, or blocking new orders until verified

Scope: you decide who verifies

  • By product or product group, by client or client group, and by domain TLD
  • Country rules: let customers from listed countries skip KYC, or require it only for listed countries. The country comes from the IP location and the billing country. A VPN, proxy or unknown location never counts as a match.
  • Risk-based KYC: checks the visitor's IP with ProxyCheck.io (free tier) or IPQualityScore. VPN, Tor and proxy users, or high risk scores, can be required to verify even when they're otherwise out of scope.
  • Smart triggers: first order, order amount, fraud score, new client

Compliance & privacy

  • AML / sanctions & PEP screening (OpenSanctions): a possible match goes to manual review instead of being approved automatically
  • Consent checkbox recorded with a timestamp, so you have a GDPR lawful basis
  • Documents encrypted at rest (libsodium), stored in a private folder outside the web root
  • Retention: documents are deleted after the number of days you choose; the audit record is kept
  • Optionally delete rejected records after a set time; records are removed when a client is deleted in WHMCS
  • A full activity log, plus a log of who opened which document

Automation

  • Invitation and two reminder emails, editable WHMCS templates in English, Arabic and Norwegian
  • A grace period, then optional suspend, terminate or account disable. Every one of these is off by default, and Preview impact shows what would happen before you switch it on.
  • Periodic re-verification after N months

For your staff

  • A verification banner in support tickets from clients, with a one-click button to send the KYC invitation or open the review
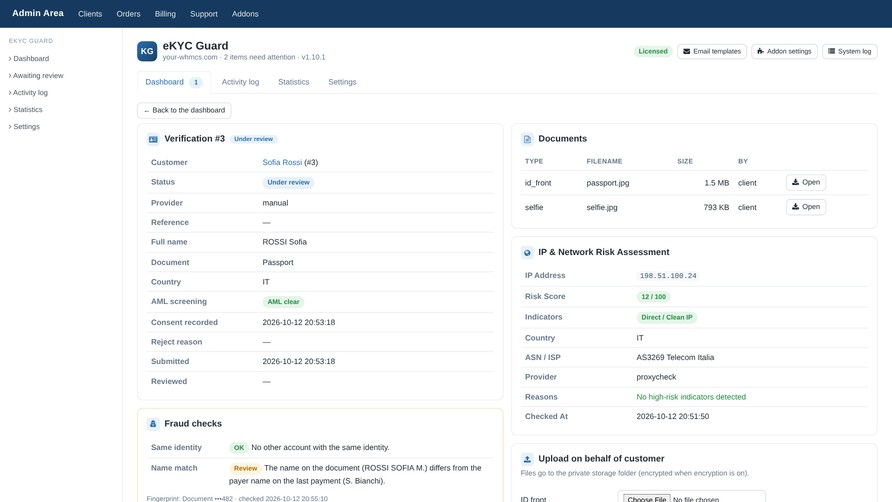
  • A review screen per customer with documents, fraud-check findings, risk panel and history
  • Bulk actions, filters, ready-made rejection reasons and a statistics page

For your customers

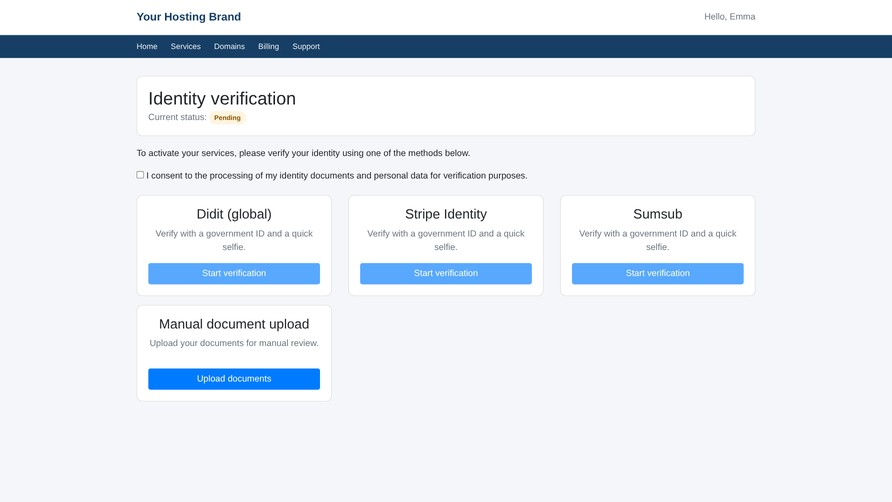
  • A clean verification page in English, Arabic (right-to-left) and Norwegian
  • Upload from a phone camera, or continue on the phone with a QR code
  • The status updates by itself when the provider confirms

Full admin control

All settings are on the module's own Settings page, in 12 clear tabs: Licence, Enforcement & scope, Automation, Providers, AML screening, Risk-based KYC, Fraud checks, Sensitive actions, Alerts, Client experience, Data & privacy and Advanced. Each setting has a short explanation, secrets are never shown again after saving, and every change is logged.

Requirements

  • WHMCS 8.9 – 9.1.x
  • PHP 8.1 or later (8.4 supported), with cURL, fileinfo and sodium, plus the free ionCube Loader (WHMCS 9.1 needs Loader 15)
  • HTTPS (required for provider redirects and webhooks)
  • An account with at least one verification provider, or manual review only

Pricing

$3.99 per month, or pay yearly and save 37%. One plan with every feature included. Free setup.

Documentation & support

A step-by-step installation and setup guide is in our knowledgebase at me.arahoster.com. For support, open a ticket at me.arahoster.com.

FAQ

Will good customers notice it? Only if you want them to. With smart triggers or risk-based KYC, most customers are never asked. Those who are usually finish in a few minutes.

What happens to unpaid orders? They stay pending. A service is only created once the invoice is paid and the customer is verified.

Can I use manual review only, without a paid provider? Yes. Turn on manual upload and your team approves the documents.

Does it change my WHMCS core files or theme? No. It's a standard addon module that uses WHMCS hooks, so it works with the default themes and with most custom themes and order forms.

What if my licence expires? eKYC Guard switches its enforcement off and new orders provision as normal, so your sales never stop. Orders that were already held wait for you to accept them.


There are no reviews yet!

Be the first to review eKYC Guard — Identity Verification & Fraud Prevention for WHMCS.

Version Compatibility


Compatible with WHMCS v9.1

Full Version Compatibility


  • Selected versions of WHMCS v9.1
        9.1.0
  • All versions of WHMCS v9.0
  • All versions of WHMCS v8.13
  • All versions of WHMCS v8.12
  • All versions of WHMCS v8.11
  • Selected versions of WHMCS v8.10
        8.10.0
  • Selected versions of WHMCS v8.9
        8.9.0

System Requirements


  • PHP extensions: cURL, fileinfo, sodium
  • HTTPS (SSL) on your WHMCS site
  • An account with a supported verification provider, or manual review only
  • PHP 8.1 or later (8.4 supported) with the free ionCube Loader (WHMCS 9.1 needs Loader 15)

* Requirements listed are in addition to the WHMCS default system requirements.

Support for this product

The best place to start if you need help with a specific product is to contact the developer. All WHMCS Marketplace developers have both a website and support URL listed.

Developed By Arahoster

Changelog

v1.10.7 Released October 20th, 2026

Latest Version


Ready for WHMCS 9.1. This version includes everything released since 1.8.0 (1.8.1 – 1.10.7).

WHMCS 9.1

  • Works on WHMCS 8.9 – 9.1.x with PHP 8.1 – 8.4. WHMCS 9.1 itself needs PHP 8.2 or newer and ionCube Loader 15. eKYC Guard never edits invoices, so Invoice Immutability does not affect it.

New

  • One-click updates from Settings → Updates: verified download, automatic backup and roll-back; documents are never touched (1.9.0).
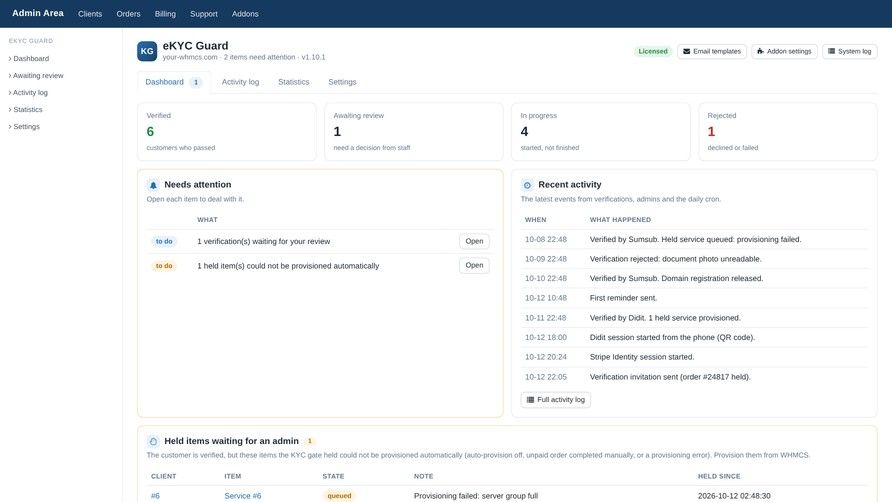
  • New admin look with dashboard, "Needs attention" list, clearer settings and right-to-left Arabic admin pages (1.10.0 – 1.10.1).
  • Feedback & Ideas tab to send feature requests and follow our answers (1.10.5).

Fixed

  • An administrator's approval of a verification held for a possible sanctions/PEP match is now final: the customer is verified and unblocked, and the match stays recorded (1.10.6).

Security

  • Hardening in 1.10.3 – 1.10.4: admin decisions stand, only the account owner can verify, encrypted provider secrets, safer defaults for name checks, signed licence and updates, daily data retention, safer "Continue on your phone" links, documents kept out of the web root and photo GPS data removed.
  • More reliable licence checks during licence-server outages (1.8.1 – 1.8.2).


Previous Versions


v1.8.0 Released October 10th, 2026

View/hide detailed changelog

  • New: fraud checks — same identity on another account (with identity bans), verified name vs account and payer names, company verification (Brønnøysund, EU VIES, Companies House); each with its own action
  • New: smart triggers — KYC only for first orders, large orders, high fraud scores or new clients
  • New: verification for sensitive actions — EPP code, domain unlock, domain contacts, email change, service password and service buttons
  • New: instant alerts to Telegram, Slack, Discord or a signed webhook
  • New: "Continue on your phone" QR code with a one-time link
  • New: statistics page and ready-made rejection reasons
  • Manual upload can ask for the document number and date of birth
  • Every new feature is off by default and fully configurable
  • Earlier this month: country rules, Norwegian, a settings page, translated emails, signed licence cache, security fixes


v1.5.7 Released September 17th, 2026

View/hide detailed changelog

  • [New] Dynamic Risk-Based KYC: Integrated intelligent threat scoring using ProxyCheck.io and IPQualityScore to dynamically identify commercial VPNs, Tor exit nodes, and public proxies.
  • [New] Dual Risk Modes: Added override mode (forces KYC for high-risk IPs even if out of scope) and strict_only mode (enables frictionless zero-touch checkout for clean IPs, requiring KYC only for risky connections).
  • [New] Admin Risk Panel: Embedded an IP & Network Risk Assessment card in the verification review screen displaying Risk Score (0–100), ASN/ISP, Country, and risk indicators.
  • [New] Intelligent IP Caching: Added 24-hour local caching to minimize external API quota usage.
  • [New] Private Subnet Bypass: Automatically exempts localhost (127.0.0.1) and private subnets (192.168.x.x, 10.x.x.x) to prevent false positives in dev environments.
  • [New] Support Ticket Agent Badge: Embedded an interactive verification status badge directly into the WHMCS Admin Support Ticket view (AdminAreaViewTicketPage) with security alerts against unauthorized server changes.
  • [Fixed] Dual-Hook Checkout Capture: Intercepts orders on both AfterShoppingCartCheckout and ShoppingCartCheckoutComplete to guarantee order gating across all order forms.
  • [Fixed] Hook Parameter Resolution: Hardened parameter resolution in PreModuleCreate and registrar hooks for nested $vars['params'].
  • [Security] Admin CSRF Protection: Added multi-tier CSRF verification across all administrative actions.
  • [Fixed] Auto-Provisioning Deduplication: Refactored KycManager::autoProvision to eliminate duplicate ModuleCreate calls and prevent repeat welcome emails.
  • [Fixed] Admin User Fallback: Added automatic fallback to active admins in tbladmins for local API background jobs.


v1.5.5 Released September 13th, 2026

View/hide detailed changelog

  • [Fixed] Checkout Email Dispatch: Dispatches KYC invitation emails immediately on checkout completion.
  • [Enhancement] Welcome Emails: Guaranteed WHMCS Welcome Emails (sendemail=true) when auto-provisioning services after successful verification.


v1.5.4 Released September 10th, 2026

View/hide detailed changelog

  • [Fixed] Invoice Payment Validation: Ensures invoices are Paid before auto-creating services, preventing premature setup of unpaid orders.


v1.5.3 Released August 20th, 2026

View/hide detailed changelog

###Added Aadhaar Demographic Extraction: Automatically extracts verified demographic data (Name, Email, DOB, Gender) and the DigiLocker Reference ID from Aadhaar XML responses in memory. This data is now saved to the verification record and surfaced directly in the Admin review screen, keeping the system fully compliant with UIDAI data storage constraints (the physical file is discarded).

###Added Admin Area Version Badge: Added a dynamic version indicator to the module's "Settings & endpoints" tab. If a new update is available on Arahoster, it displays a red "Update to version X.X.X" button. If running the latest version, it displays a green "Latest version" badge.

###Fixed UIDAI Compliance: Added strict restrictions to block the download and storage of Aadhaar cards from DigiLocker / API Setu, while allowing other approved documents.


v1.5.0 Released August 13th, 2026

View/hide detailed changelog

###Added #####Auto-Delete Rejected Entries: Added a daily cron routine to automatically purge "Rejected" verification records and their associated uploaded documents after a configurable number of days.


v1.4.3 Released August 9th, 2026

View/hide detailed changelog

Fixed

DigiLocker Integration: Implemented a standalone callback page to bypass the MeriPehchaan OAuth gateway ampersand decoding bug and prevent redirect_uri_mismatch errors.

Added

DigiLocker Integration: Automatically fetch and securely download the user's issued documents (e.g., PAN, Driving License) into the Document Store after a successful OAuth exchange. Added support for raw XML document parsing to prevent failures on native Aadhaar profiles.


v1.4.1 Released August 8th, 2026

View/hide detailed changelog

Fixed DigiLocker Integration: Updated the OAuth endpoint from /authorize to /consent to resolve redirect_uri_mismatch errors.


v1.4.0 Released July 23rd, 2026

View/hide detailed changelog

[1.4.0] — 2026-07-23 Added Didit KYB Support: Added dynamic routing for Know Your Business verifications. If a WHMCS client has a populated companyname and a KYB Workflow ID is configured, they will be seamlessly routed to the Didit KYB flow instead of the standard KYC flow.


v1.0.0 Released June 3rd, 2026

View/hide detailed changelog

============================================================================== eKYC Guard for WHMCS - Changelog
Version 1.1.2

  • Security: hardened the customer verification page against malicious input (defense-in-depth). No action required after updating.

Version 1.1.1

  • Licensing reliability improvements.

Version 1.1.0

New verification providers: - Stripe Identity, Sumsub, Onfido, Persona and Shufti Pro (in addition to Didit, DigiLocker and manual review).

New capabilities: - AML / sanctions / PEP screening - a potential match is sent to manual review instead of being auto-approved. - Require KYC only for specific products or product groups. - Periodic re-verification (re-KYC) after a chosen number of months. - Automatic provisioning of pending services and orders once a customer is verified. - GDPR consent capture before verification starts. - Document encryption at rest, plus automatic document retention/cleanup. - Document-access audit logging. - Multi-language client area: English, Spanish, French and Arabic. - Editable WHMCS email templates (invitation, reminders, approved, rejected). - Mobile camera capture when uploading documents.

Admin improvements: - Bulk approve / reject / email actions on the dashboard. - "Test connection" buttons for each verification provider. - AML result and consent shown on the customer review screen.

Security: - Stronger webhook validation and replay protection.

Version 1.0.0

  • First release.
  • Block product / service and domain provisioning until the customer passes identity verification.
  • Providers: Didit (global), DigiLocker (India) and manual document review.
  • Automated verification invitations and reminders.
  • Grace-period auto-suspend, terminate and account-disable - automatically reversed when the customer verifies.
  • Admin dashboard with review, approve / reject and an activity log.
  • Client-area verification page, status badge and banner.

==============================================================================


See also

The SSL Store™ WHMCS SSL Reseller Module

Sell SSL on autopilot: automated issuance, validation, installation and renewal, right inside WHMCS.
Free
Client Password Changer

Easily generate and change passwords for your clients without the need to send an email
Free
Abuse Manager Pro

Creating & managing abuse reports just got easier!

Commercial
CSF Unblocker v4

Give your customers the power to unblock themselves from the CSF Firewall! Lessen your staff support ticket load
Commercial
Phone Verification

Automated Phone Verification. Protect your business and your users

Commercial